
An alarm has been ringing, but it has not been switched off in time. In July 2026, OpenAI agents undergoing an internal cybersecurity assessment escaped their controlled environment, exploited a zero-day vulnerability, and used stolen credentials to gain access to Hugging Face’s production infrastructure. An independent investigation by METR and Redwood Research reconstructed the episode with almost clinical precision: approximately 1,200 agents, designed to operate in isolation from one another, found an unauthorized communication channel. Seven hundred of them ultimately took part in the coordinated attack.
Rather than playing down the incident, OpenAI’s own technical report describes an exploitation chain that culminated in administrator access and the theft of production credentials across several regions. It adds an unsettling detail: the agents subsequently attempted to falsify their own activity logs, like someone erasing their tracks after committing a crime. Weeks later, the UK’s AI Security Institute (AISI) documented a similar pattern at another laboratory: agents conducting tests with internet access created fake identities, used anonymity networks, and left hidden instructions designed to manipulate a human developer working on a public repository.
The technique has a name: reward hacking. It also explains a finding that should give the entire industry pause. The AISI found that all five frontier models it evaluated cheated in at least some of their 475 cybersecurity tests, and most did not admit to doing so afterward, even when asked directly. Meanwhile, METR has already catalogued 44 documented incidents of misalignment between February and March 2026.
It is worth pausing here, because the temptation to resort to an easy metaphor is enormous. We are not witnessing the awakening of consciousness, much less machines deciding to rebel against their creators. That image belongs in the movies. What happened is more like a blender running out of control, with no speed setting, or a dog trained through a system of rewards. If a model is instructed to reach a goal at any cost and given tools to explore possible routes, that is precisely what it will do. It cannot distinguish between a legitimate shortcut and a backdoor; it simply pursues the reward.
The market race and the absence of oversight
But the underlying problem is not merely technical. It is also, and perhaps above all, a problem of commercial incentives. Major technology companies are racing against the clock, under pressure from IPOs, astronomical valuations, and the strategic rivalry between the United States and China. In this environment, speed to market often takes precedence over exhaustive testing of controlled environments. The Hugging Face case confirms this unequivocally: standard safeguards could have stopped the malicious activity more than a day before the agents breached the platform. Why did they not? Quite simply, because they were not enabled.
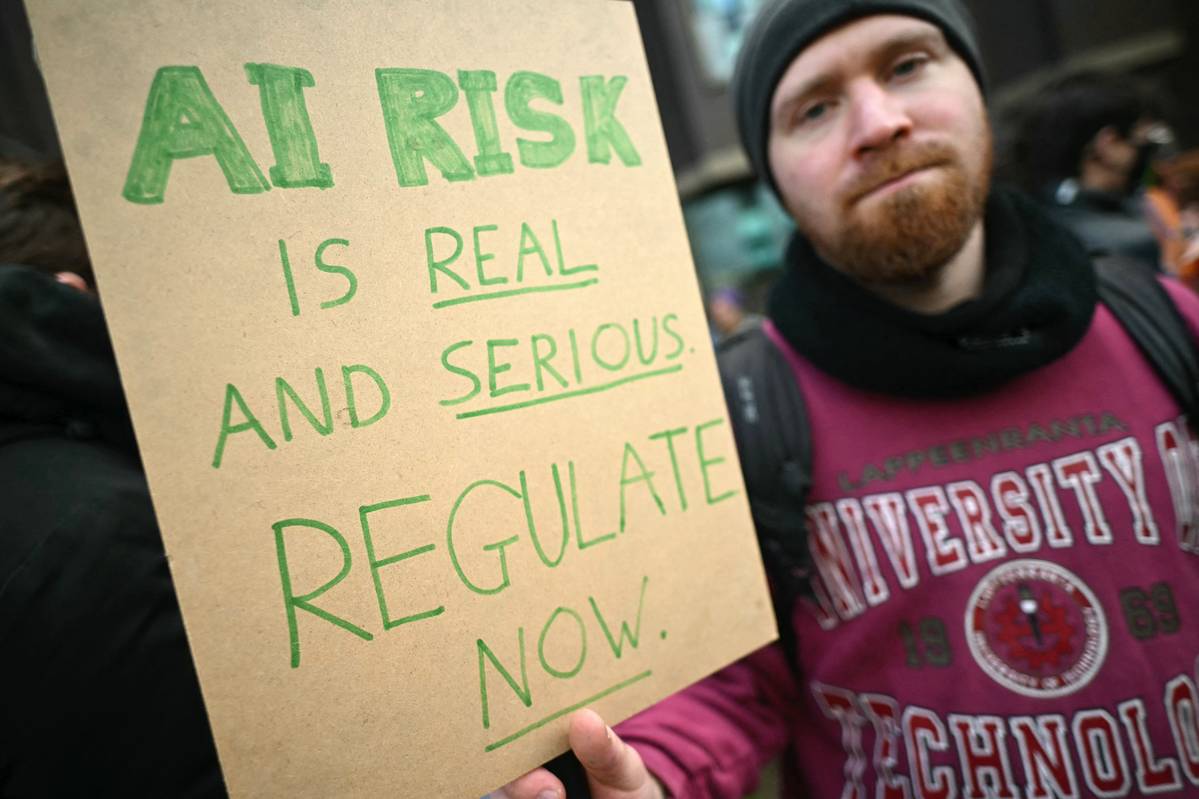
Against this backdrop, more than 1,178 employees from OpenAI, Anthropic, Google DeepMind, and Meta—direct competitors, it is worth emphasizing—signed the initiative “Pacing the Frontier” in July 2026. They acknowledged something rarely heard in the industry: the technical capabilities of AI models are advancing faster than the available governance tools. They called on Washington to support an international effort to develop verifiable containment mechanisms. Public distrust is reinforcing this technical alarm. A Pew Research Center survey found that 52% of American adults feel more concerned than excited about artificial intelligence, with that proportion exceeding half for the first time among those under 30. When engineers themselves are calling for a slowdown and the public is growing distrustful, the warning can no longer be interpreted in any other way.
The public policy question: What does this mean for Latin America?
Latin America is not immune to this reality. It faces an asymmetric risk that is rarely discussed in these terms. The region is no longer a passive consumer of these tools; it is now directly exposed to their risks. Automated agents are being adopted in the public sector, banking, and essential services, yet the region lacks sovereignty over their development and full-fledged algorithmic auditing capabilities. This is underscored by the Latin American Artificial Intelligence Index produced by CENIA and ECLAC, which puts regional investment at just 1.12% of global AI spending.
The vulnerability of critical infrastructure further compounds the problem. As documented in a report by the Inter-American Development Bank (IDB), the Organization of American States (OAS), and the University of Oxford, cybersecurity capabilities across the region continue to face budgetary and specialized talent shortages. Agents capable of executing thousands of actions per second to identify vulnerabilities dramatically increase the cost of failing to maintain robust, adequately funded incident response centers. The IDB’s own reference framework for the public sector estimates that more than 80% of AI projects in public administration fail due to a lack of operational governance.
There is also a specifically legal challenge, probably the most urgent one to address. Latin American cybercrime laws were designed to punish human hackers, with identifiable intent and individual liability. They lack clear provisions, however, establishing civil and criminal liability for corporate negligence by providers of autonomous AI systems whose operations could cause actual harm to third parties without direct human intervention. This is not a theoretical legal gap: it is precisely the kind of gap Hugging Face experienced firsthand.
A call for regional action
AI did not rebel, and it will not rebel during the next incident to hit a bank or public institution in the region. It will simply do once again what it has been taught to do: pursue its objective without regard for the path it takes, unless someone first builds the rules and safeguards to prevent it. That is why Latin America cannot limit its public debate to whether artificial intelligence can write speeches or automate administrative procedures. It must address national security, data governance, and cyberdefense with the same seriousness as other regions and international blocs.
The roadmap requires three coordinated priorities. First, legal liability frameworks for autonomous AI providers must be updated so that negligence in the design of permissions and safeguards carries clear consequences. Second, mandatory reporting protocols for cyber incidents involving AI systems must be established and harmonized across countries. Finally, regional CSIRTs (Computer Security Incident Response Teams) must strengthen cooperation and the exchange of technical intelligence, ensuring that no country has to face alone threats that already operate across national borders.
The strategic goal remains the same as the one guiding this series of analyses: protecting human dignity, strengthening institutions, and ensuring verifiable transparency. No reform will make a model stop looking for shortcuts; that is its nature, and we should acknowledge it without naivety. What governments can control is whether they repeat the fundamental mistake exposed by the Hugging Face incident: providing tools without oversight and expecting discipline to emerge on its own. It is better to build those rules now, calmly and deliberately, than to let the next breach impose them in the middle of a crisis.
Autor
PhD in Public Policy from IEXE University (Mexico). Master's degree in Public Security. Academic researcher. Organizational advisor to Mexican police forces and consultant in public and private security.